Data stays in the fab
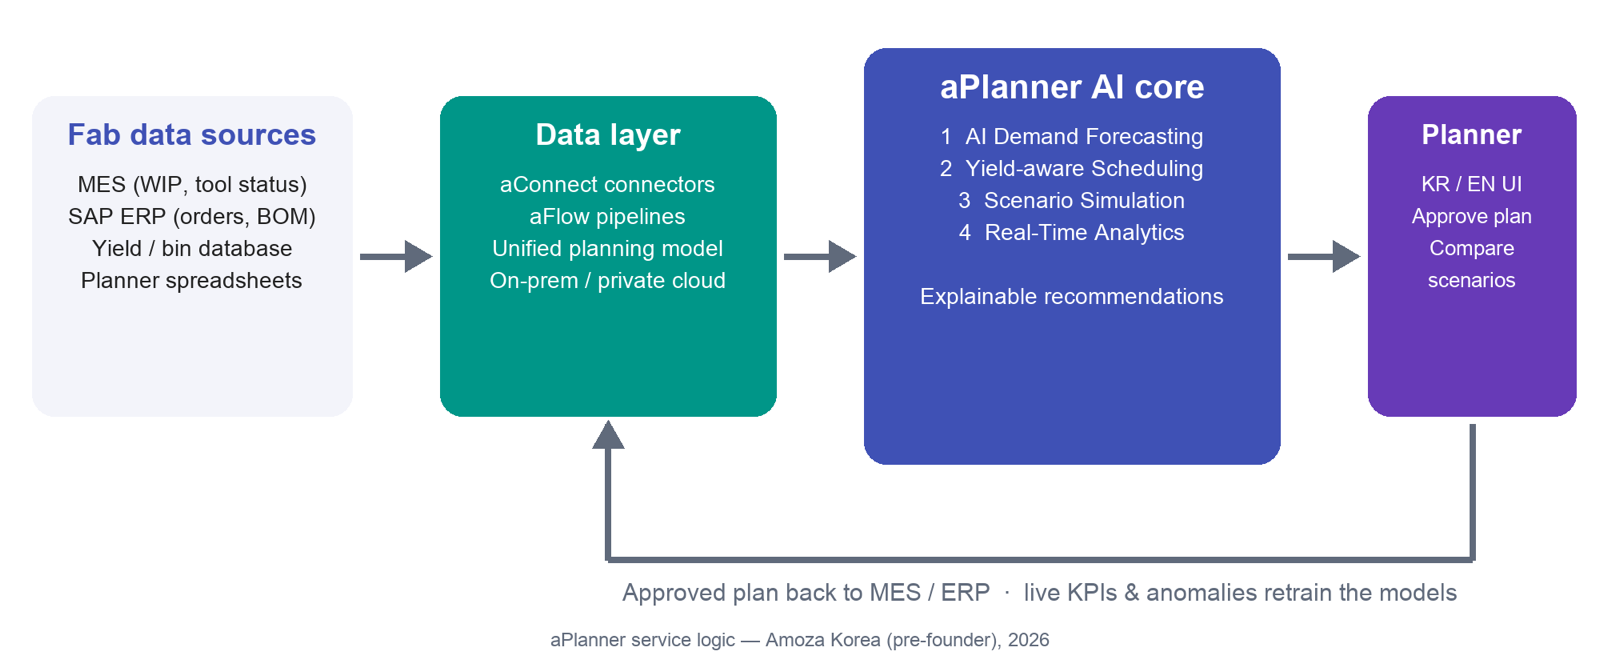
Korean fabs reject off-site production data. aPlanner is designed on-premise / private cloud first, with read-only connectors, role-based access, SSO and a full audit trail — and an honest compliance roadmap.
Deployment options
Same Kubernetes packaging, same code everywhere — the fab chooses where it runs.
On-premise
Private cloud
SaaS — AWS Seoul region
Compliance roadmap
No certification is claimed before it is earned. Status labels below are the current plan (October 2026).
Encryption at rest and in transit
RBAC, SSO, audit trail
SOC 2 Type II
ISO 27001
K-ISMS
Korean PIPA notice
Security & governance
Role-based access control
Planner, approver, viewer and admin roles with granular permissions per site and plan.
Single sign-on
SAML 2.0 / OIDC against the fab’s identity provider; no separate passwords.
Immutable audit trail
Every plan change carries its trigger, constraints, the planner’s reason and who was notified.
Planner-approval workflow
AI recommends, people decide. Frozen-zone overrides require explicit acknowledgement.
Read-only first
Connectors start read-only; write-back to MES / ERP is enabled only after sign-off.
No employer or customer data
The MVP is built on public methods and synthetic data; customer data stays inside the customer’s deployment.
Python / FastAPI · PostgreSQL + TimescaleDB · OR-Tools / MILP (CP-SAT) · PyTorch, XGBoost · React (KR / EN) · Kubernetes on-prem or AWS Seoul
Questions about security or deployment?
Talk directly to the founder about on-premise deployment, connectors and the compliance roadmap for your fab.